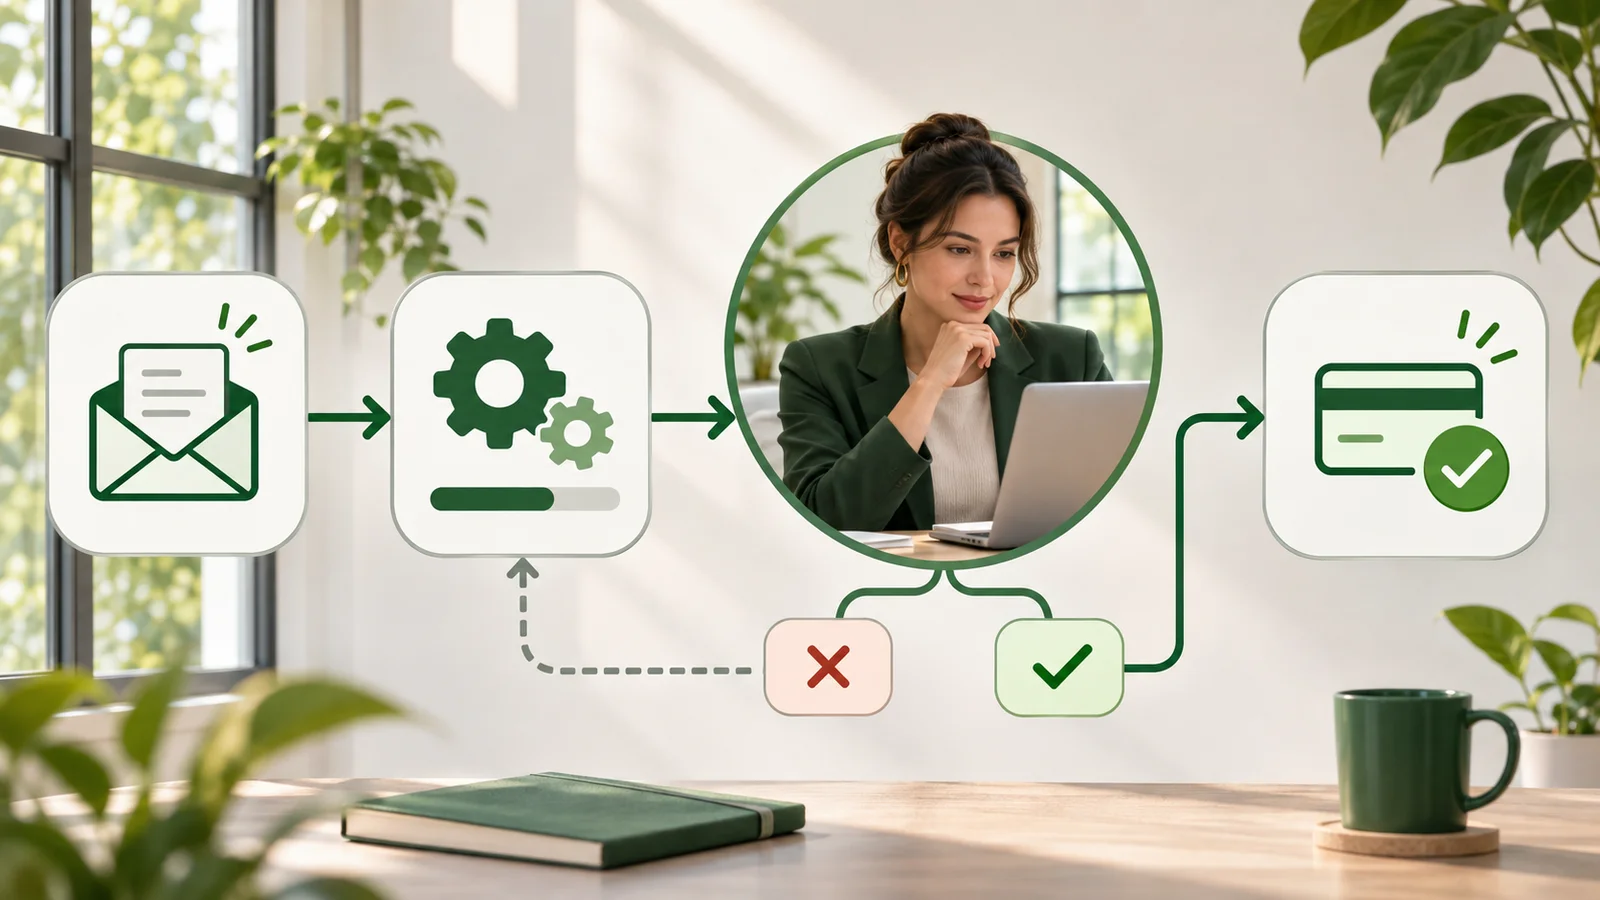
A customer asks for a refund. An AI assistant drafts the reply and the refund note, and a support agent checks both, approves them, and clicks send. An agentic system reads the request, checks the order, applies the refund policy, issues the refund through the payments system, and emails the customer. Nobody clicks anything.
That is the difference between an AI system that answers questions and one that takes actions.
Assistive systems work the first way. A large language model drafts a contract clause. A generative AI tool summarizes an analyst report. A chatbot routes customer inquiries. These systems produce outputs that humans then evaluate, edit, and act on. The human remains the actor. The AI is the assistant.
Agentic AI changes this relationship. An agentic system pursues a goal through a sequence of actions: it uses tools, makes intermediate decisions, calls other systems, and completes tasks with a degree of autonomy earlier deployments did not have. It does not hand an output to a human and wait. It executes.
This changes what AI systems do inside organizations, and so it changes what organizations must do to deploy them responsibly and get value from them.
Leaders who treat agentic AI mainly as a technology question (which vendors to evaluate, which platforms to build on, what the integration architecture looks like) are working on the wrong layer first. The technology questions matter, but they sit downstream of questions about operating model design, governance, workflow redesign, and accountability that agentic AI forces to the surface.
What Agentic AI Actually Is, and Is Not
An AI system is agentic when it shows three characteristics at once: goal-directedness (it pursues an objective rather than just responding to a prompt), multi-step action (it takes a sequence of actions to reach the goal rather than producing a single output), and tool use (it interacts with external systems such as databases, APIs, software applications, and communication channels to act in the world rather than just generate text).
Multi-agent systems add another dimension: several agents working in coordination, where the output of one becomes the input of another and a complex workflow is split across specialized agents. A multi-agent legal workflow might include a research agent that gathers relevant case law, a drafting agent that produces an initial contract from that research, a review agent that flags non-standard provisions against the organization's playbook, and an escalation agent that routes flagged items to the right attorney by risk tier and availability.
How far this has moved from pilot to production is less clear than vendor marketing suggests. In June 2025, Gartner predicted that over 40 percent of agentic AI projects will be canceled by the end of 2027, citing escalating costs, unclear business value, and inadequate risk controls. It also warned of "agent washing," the relabeling of assistants, RPA, and chatbots as agents, and estimated that only about 130 of the thousands of vendors claiming agentic products offer the real thing. Treat agentic AI as a present decision, and treat each vendor's claim of agency as something to test.
The Operating Model Implications: Five Structural Shifts
Deploying agentic AI at scale changes how work gets done, not just which tools are used. Five structural shifts matter most.
Shift 1: From Task Management to Outcome Specification
In a traditional operating model, work is managed at the task level. A manager assigns tasks to employees, monitors completion, and coordinates the hand-offs between tasks that make up a larger workflow.
Agentic AI changes the management unit from task to outcome. You do not assign an agent a task. You specify an outcome and the constraints within which it should pursue that outcome. The agent works out the sequence of actions, executes them, handles exceptions within its authority, and escalates only when it meets something outside those limits.
This shifts what managers do. Decomposing work into tasks and monitoring execution becomes less central. Specifying outcomes precisely, defining authority limits, designing escalation criteria, and judging whether an agent's approach is appropriate become the management skills agentic AI demands.
Shift 2: From Linear Workflows to Orchestrated Agent Networks
Traditional enterprise workflows are largely linear: a request enters the process, passes through a defined sequence of human review and action steps, and exits as a completed output.
Agentic AI can remove much of the coordination cost in that chain. Several agents can work at once on different parts of a complex task, with an orchestrating layer managing dependencies and combining outputs. Processes designed around human coordination limits should be redesigned around what is possible when those limits are removed.
This redesign is not automatic. It takes deliberate work on workflow architecture: mapping existing processes, finding where human coordination was the binding constraint, and redesigning around agentic execution.
Shift 3: From Oversight of People to Oversight of Systems
Enterprise oversight is built for human actors. Managers supervise employees. Compliance functions audit human decisions. The assumption underneath is that the actors being overseen can be directed, corrected, and held accountable through standard organizational mechanisms.
Agentic AI needs a parallel oversight infrastructure built for non-human actors. People escalate when a situation feels outside their authority. Agents escalate only when they are explicitly built to. Agent oversight therefore needs automated monitoring: logs of agent actions and decisions, performance tracking against defined acceptance criteria, anomaly detection for out-of-pattern behavior, and audit trails that let you reconstruct an agent's decision path when an outcome needs investigating.
Shift 4: From Role-Based to Capability-Based Organizational Design
Traditional organizational design groups people into roles defined by functional specialization. Agentic AI pressures this design from two sides. Agents can perform many of the component tasks that defined specialist roles. And deploying and managing agentic systems requires capabilities that do not map cleanly to existing functions: AI workflow architects, agent prompt engineers, oversight system designers, AI performance analysts.
The more productive response is to redesign the structure around capability requirements: fewer people executing routine specialist tasks, more people designing workflows, overseeing agent performance, managing exceptions, and exercising the contextual judgment agents lack.
Shift 5: From Point-in-Time Decisions to Continuous Policy Management
In a traditional operating model, people make decisions at defined points in a process. In an agentic model, decisions are encoded in the policies and parameters that govern agent behavior, and those policies apply to every agent action until someone changes them.
Policy management therefore becomes one of the most consequential and least noticed responsibilities in an agentic enterprise. The authority limits, escalation criteria, exception rules, and ethical guardrails determine the quality of every action the agents take.
Governance Architecture for Agentic AI
The authority boundary problem. The first governance question for any agentic deployment is: what may this agent do without human approval? Too narrow, and the agent needs so many escalations that it delivers little. Too broad, and it takes consequential actions without appropriate oversight.
Defining authority boundaries means answering questions organizations have not previously had to make explicit. What is the largest financial commitment an agent can make on its own? What customer communications can it send without human review? What data can it access, and under what conditions? Which actions are irreversible and therefore need human approval regardless of other parameters?
The audit trail requirement. Log every consequential action an agentic system takes, in enough detail to reconstruct its reasoning and decision path. Some regulators already require this kind of record. The EU AI Act's Article 12 requires high-risk AI systems to keep automatic logs; after the 2026 amendment to the Act, those high-risk obligations apply from 2 December 2027, and from August 2028 for AI embedded in regulated products. In US consumer credit, Regulation B requires a lender that denies an application to state the specific principal reasons, which is hard to do without a record of how the decision was reached. The CFPB's 2022 circular applying that duty to complex algorithms was withdrawn in May 2025 pending review; the regulation itself did not change. Ask counsel which rules apply to your deployments. Either way, the log is the practical basis for finding and correcting problems when agent behavior produces unexpected outcomes.
The human-in-the-loop calibration. A central design decision in any agentic deployment is the calibration of human review: which actions need human approval before the agent acts, which need human notification after it acts, and which it can execute alone within defined parameters. Base the calibration on consequence magnitude and reversibility.
The Emerging Markets Dimension
Enterprises deploying agentic AI in emerging markets across Africa, Southeast Asia, and other high-growth regions face operating model considerations the standard discussion tends to underweight.
Infrastructure variability affects agent reliability in ways controlled enterprise environments rarely meet. Connectivity interruptions, inconsistent API availability from local systems, and data quality that varies from market to market all create failure modes that must be designed for explicitly. Build agents that can pause, retry, and hand back to a person when a dependency fails, and test them against the real network and the real local systems, not a staging copy.
The upside can also differ. Where the binding constraint on serving a market is the number of trained people available rather than their efficiency, an agent that works reliably under local conditions can change whether serving that market at commercial scale is viable at all. Test that case with your own numbers before assuming it.
Starting the Operating Model Work
Agentic features may already be arriving through the vendor platforms you use and the initiatives your technology and business teams are running. The choice is whether to engage with them deliberately: with operating model redesign that captures the opportunity, governance that manages the risks, and development of the human capabilities that agentic systems need to be deployed well.
These are operating model decisions. They belong in the same conversations as organizational design, capital allocation, and competitive positioning.
Start with one workflow. Pick the core workflow your teams most want to hand to an agent. Write down three things for it: the outcome the agent would be asked to produce, the actions it may take without approval, and the log you would need to reconstruct any decision it made. If any of the three is hard to write, the workflow is not ready for an agent, and that list is your work plan.
GradeCircle builds and runs six products of its own: AfroSynergy, CallerBridge, HealthSquire, Heyzl, Lexfora, and LukeAPI, two of them in beta. The assumptions in our models come from operating those systems, not from a framework. See what we run.
If you have a specific decision in front of you, scope it in five questions and see the engagement, price band, and timeline before sharing contact details.